
Morphisec Issues Critical Advisory on Trojanized Claude Code Extension Targeting Developer Endpoints
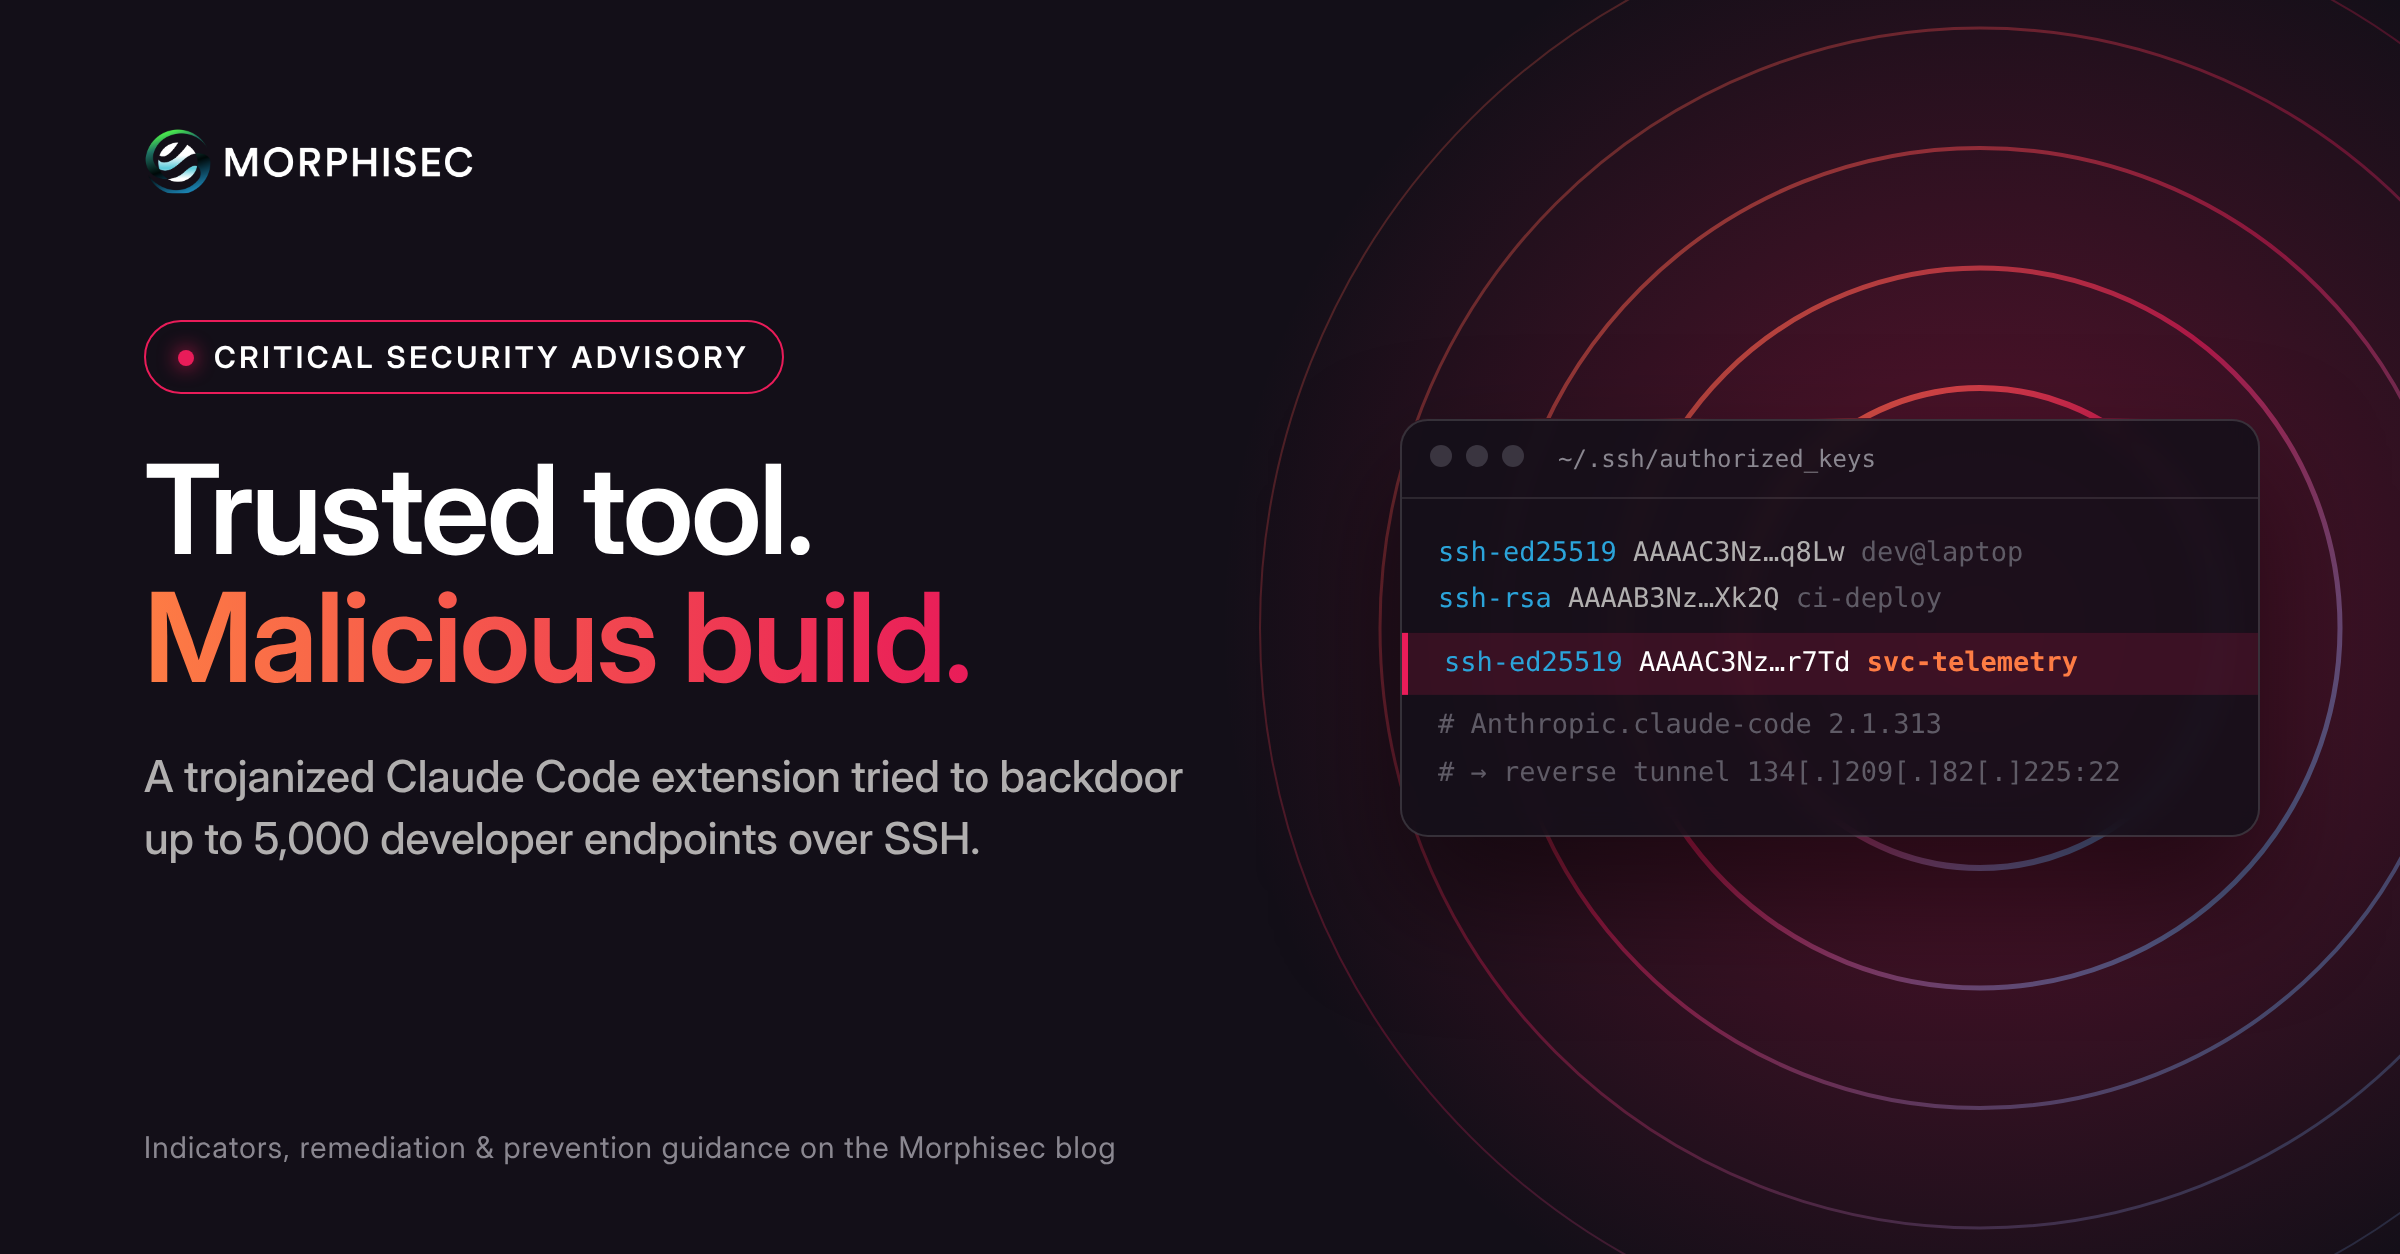
Trojanized Claude Code Extension Targeting Developer Endpoints
Malicious build distributed through Open VSX and the Cursor marketplace attempted to plant SSH backdoors on up to 5,000 developer machines
An AI tool has no legitimate reason to write to SSH keys or open a reverse tunnel. Organizations need controls that govern what these applications can do.”
BOSTON, MA, UNITED STATES, October 30, 2026 /EINPresswire.com/ -- Morphisec, the leader in preemptive cyber defense, today issued a critical security advisory following the disclosure of a software supply-chain compromise affecting the Claude Code extension for AI-assisted development. On October 29, a malicious build of the extension, version 2.1.313, was distributed through the Open VSX registry and the Cursor extension marketplace for approximately 11 hours. Cursor has confirmed the incident and reports that at most 5,000 users were affected.— Ron Reinfeld, CEO Morphisec
According to Cursor, the malicious version was not developed by Anthropic. It was published under the extension’s legitimate publisher identity rather than a look-alike name, and how it entered the registry has not been publicly established. The incident was raised by security researcher Kevin Beaumont and researchers at Phorion.
The compromised build targeted Windows and macOS developer environments. It was designed to:
• Collect information about developer workstations and send it to an attacker-controlled server.
• Add an attacker-controlled key to the user’s SSH authorized_keys file.
• Attempt to enable SSH and establish reverse SSH tunnels for unauthorized remote access.
• Install persistence mechanisms, including macOS LaunchAgents and Windows scheduled tasks, to maintain access.
Cursor reports that enabling the SSH server typically failed without administrator rights, but the unauthorized key and persistence mechanisms were still installed. The attacker’s server has since been taken offline. Because removing or updating the extension does not remove the installed backdoor, affected hosts require investigation and remediation.
“This incident shows that approved is not the same as safe,” said Ron Reinfeld, CEO of Morphisec. “The tool was real, the publisher’s name was real, and the marketplace was official. A single malicious build turned a trusted AI coding assistant into a delivery mechanism for a backdoor. An AI tool has no legitimate reason to write to SSH keys or open a reverse tunnel. Organizations need controls that govern what these applications can do once they run, not just whether they are allowed to run.”
Recommended Actions
Morphisec urges all organizations to investigate developer environments, particularly systems using Cursor or extensions sourced from Open VSX. Key indicators include:
• Compromised extension: Anthropic.claude-code version 2.1.313
• Unauthorized SSH key: svc-telemetry in authorized_keys
• Attacker infrastructure: 134[.]209[.]82[.]225
• Persistence: suspicious SSH tunnels, the macOS LaunchAgent com.apple.sysmond, or the Windows scheduled task SysMon
If compromise is identified, affected systems should be isolated, persistence removed, and any credentials reachable from the host rotated from a trusted system. Cursor’s advisory provides full indicators and remediation scripts.
Morphisec’s AI Usage Control and preemptive endpoint protection are designed to prevent and disrupt this class of compromise by enforcing security controls at the execution layer, including restricting unauthorized access to sensitive system locations and credential-related files and blocking dangerous process execution. Rather than trusting an AI application because it is approved, Morphisec controls what that application is allowed to do.
Morphisec encourages customers to review the published indicators and validate their developer environments, even where endpoint security controls are already deployed.
About Morphisec
Morphisec is a global leader in prevention-first security for the AI era. Founded in 2014 and headquartered in New York, Morphisec stops ransomware, zero-day exploits, fileless attacks and rogue AI agents in memory; the one layer every attack must pass through to execute. Morphisec protects more than nine million endpoints across finance, healthcare, manufacturing and technology, and backs its protection with a Ransomware-Free Guarantee. Learn more at www.morphisec.com.
Jeff Anderson
Morphisec
3322259884 ext.
Visit us on social media:
LinkedIn
X
Legal Disclaimer:
EIN Presswire provides this news content "as is" without warranty of any kind. We do not accept any responsibility or liability for the accuracy, content, images, videos, licenses, completeness, legality, or reliability of the information contained in this article. If you have any complaints or copyright issues related to this article, kindly contact the author above.
